
The alliance could drive significant advancements in energy efficiency, potentially reshaping competitive dynamics in the tech industry. The post Nvidia, Google, Emerald AI form alliance
The Senate’s rejection of the CLARITY Act heightens regulatory uncertainty for XRP, potentially hindering its market growth and adoption. The post XRP drops 9% to
Dina Powell McCormick’s leadership at Meta could reshape tech infrastructure financing, influencing global AI competition and investment strategies. The post Meta’s Zuckerberg names Dina Powell
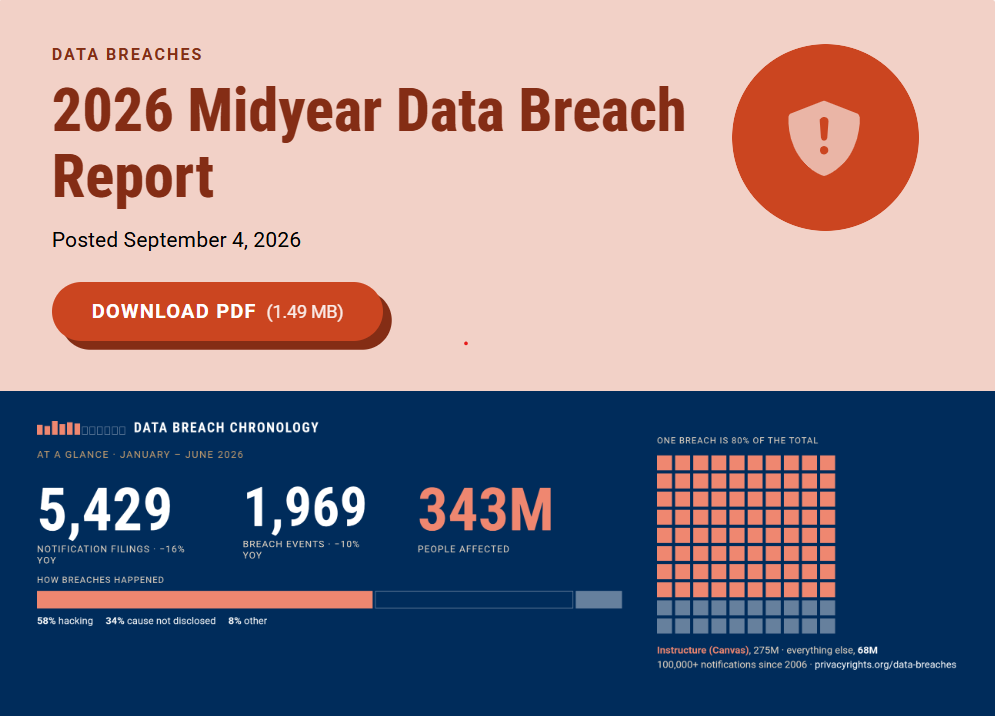
The massive theft of more than 153 million US and Canadian driver’s licenses earlier this month should make one thing abundantly clear: the safest place for a copy of your driver’s license is nowhere at all.The leaked IDs, which appear to have come from an identity verification provider, ended up on a dark web identity service dubbed Nexus, alongside millions of other stolen identity and travel documents.The danger was underscored this week after fintech Revolut revealed it had been tricked by a hacker into handing over reams of sensitive customer data, including copies of passports and verification selfies. The hacker is now drip feeding the identification documents of 680 customers onto the web in an attempt to secure a 10,000 Bitcoin ransom.The irony is hard to miss: Know Your Customer (KYC) processes are designed to make financial systems safer by establishing who customers are and making sure they’re not up to nefarious deeds. But the way KYC is usually implemented requires companies to store vast quantities of sensitive information, which creates valuable honeypots for criminals.And the problem is getting harder to ignore. In the first half of 2026 alone, US data breaches affected at least 343 million people, according to the Privacy Rights Clearinghouse. Even more frustratingly, it’s already possible to verify an individual’s identity without storing their identity documents using zero knowledge proofs:Efrat Fenigson, host of You’re The Voice podcast, writes and speaks extensively about privacy and KYC. She tells Magazine:“When regulators keep mandating a model that guarantees this outcome — while the technology to verify without storing already exists — it raises a red flag. It implies there is a lack of rational thinking and real will to solve problems.”So how many more of these leaks will it take before that will starts to bend? KYC was built to collect your identity, not just verify itKYC systems today have pretty much evolved around the assumption that institutions should see customers’ passports or driver’s licenses, record the relevant information and then store evidence of the check.343 million people have already been affected by US data breaches in 2026. Source: Privacy Rights Clearinghouse.But there’s an obvious problem with that approach: it has created a vast ecosystem of identity providers, databases, vendors and compliance systems that all store separate treasure troves of your individual KYC data. Every additional copy of your data creates another potential point of failure — and hackers are increasingly creative about devising ways to access it. In the Revolut case, the hacker sent emails requesting the KYC data from a legitimate Italian law enforcement address. Lyudmyla Kozlovska, Open Dialogue president said on X that EU laws meant Revolut had no other option but to comply.“EU AML law imposes no verification duty on the bank and provides no meaningful mechanism to check who is really behind an authenticated state request. Refusal to answer carries fines in the millions. In practice, verification is impossible.” Related: 200,000 fake AI ‘victims’ deployed to scam bait online fraudstersSusie Violet Ward, director and co-founder of Bitcoin Policy UK, warns the real issue is in storing ID data unnecessarily:“We need to stop treating identity verification and surrendering your identity as though they are the same thing.”If a company only needs to know that someone is over 18, she argues it should not automatically need additional details like your full name, address, exact date of birth, and a permanent copy of the relevant identity documents:“The irony is that KYC is designed to make systems safer, but the way we currently implement it can create an entirely different security problem. You can reset a password after a breach, but you cannot reset your identity in the same way.”The technology to stop hoarding IDs already exists For crypto proponents, the obvious solution is to use zero knowledge proofs. That’s a mathematical proof that demonstrates something is true without revealing the details. For example, you can use an phone app to generate a proof confirming your drivers license says you are older than 18, without sending through your birth date, or a picture of the license itself.Zcash founder Zooko Wilcox provides a useful explanation of ZK tech in this video. A useful explanation of ZK tech. Source: Crypto FiresideEvin McMullen, chief executive and co-founder of Billions Network, which develops privacy-preserving digital identity and ZK solutions, tells Magazine:“The technology works and is in production today, across thousands of applications and regulated institutions. What holds it back is that the entire compliance stack was built around collecting and storing copies of documents.”McMullen says the barrier was “never the technology,” but the rules, incentives and infrastructure built around it:“This is a governance and standards problem wearing a technology costume.” If the technology works, what’s stopping it?The European Union is already incorporating ZK technology into its digital identity and age verification systems design, developing privacy-preserving age verification that allows users to prove their age without revealing their full identity or exact date of birth. Related: Fears of AI-driven DeFi hack epidemic overstated for now — but not for longIts Digital Identity Wallet also supports “selective disclosure,” so users reveal only the information needed for a particular transaction. So, why isn’t this being deployed more widely for financial KYC?According to McMullen, “regulation and understanding” are the biggest obstacles to adoption:“The most common blocker is that compliance teams conflate ‘we saw the ID’ with ‘we must keep the ID,’ so they over-collect to be safe.” She says interoperability is another issue, since cryptographic proofs are only useful “if the party relying on it can check it without calling back to whoever issued it.” That requires putting shared standards in place, which is easier said than done. ZK doesn’t magically solve KYC There is another important caveat: replacing an ID document with a zero-knowledge proof doesn’t automatically eliminate every privacy or security problem.Fenigson points out that what a ZK credential remains tied to is equally important: “The incentives point toward control, not privacy. Zero-knowledge proofs let someone prove a fact, like being over 18 or not on a sanctions list […] What’s missing is what that proof gets bound to. Right now it’s usually bound to an account inside someone else’s database.” The EU’s Digital Identity Wallet supports selective disclosure. Source: European CommissionSo it boils down to who ultimately controls the credential. If a person generates a privacy-preserving proof but that proof is tied to an account in somebody else’s database, they’re still dependent on a centralized intermediary.The rules aren’t as clear-cut as you might think In many cases the rules don’t actually require storage of ID data — it’s more of a convention, because that’s the way it’s always been done.The Financial Action Task Force (FATF)’s guidance explicitly considers how digital ID systems can be used to conduct customer due diligence, rather than requiring institutions to rely on physical identity documents. FATF’s recommendations also operate as a risk-based framework, leaving individual countries to implement standards through their own legal and regulatory systems.“In many regimes, the rule is that you must verify identity and retain records of that verification, not that you must keep the raw document image forever,” McMullen says.That means a cryptographically verifiable attestation with a record showing the relevant check was performed could be enough to comply without creating another permanent copy of the ID.But because the guidance is “ambiguous,” McMullen says institutions just default to keeping everything because their compliance teams know auditors and examiners will accept it.In other words, even if the rules technically permit a different approach, nobody is willing to be the first to risk it, as Ward explains:“There is an instinct in regulation that more information means more control and therefore more safety.”It’s hard to see that changing unless the rules are amended to explicitly allow zero-knowledge proofs. And while no system is perfect, at least ZK tech prevents the need to collect and retain so much sensitive information. As McMullen says:“You cannot lose what you never held.”Magazine: 10 of the greatest unsolved crypto mysteriesCointelegraph publishes long-form journalism, analysis and narrative reporting produced by Cointelegraph’s in-house editorial team with subject-matter expertise. All articles are edited and reviewed by Cointelegraph editors in line with our editorial standards. Some articles contain affiliate links, from which Cointelegraph may earn a commission. These relationships do not influence which products we review or our editorial conclusions. Content published in here does not constitute financial, legal or investment advice. Readers should conduct their own research and consult qualified professionals where appropriate. Cointelegraph maintains full editorial independence.